Back to Eximietas Software

Digital & Intelligence Engineering · Trustworthy AI at enterprise scale

AI Security, Safety & Compliance Engineering

Security, safety, and governance controls for AI systems that influence customers, employees, and critical decisions.

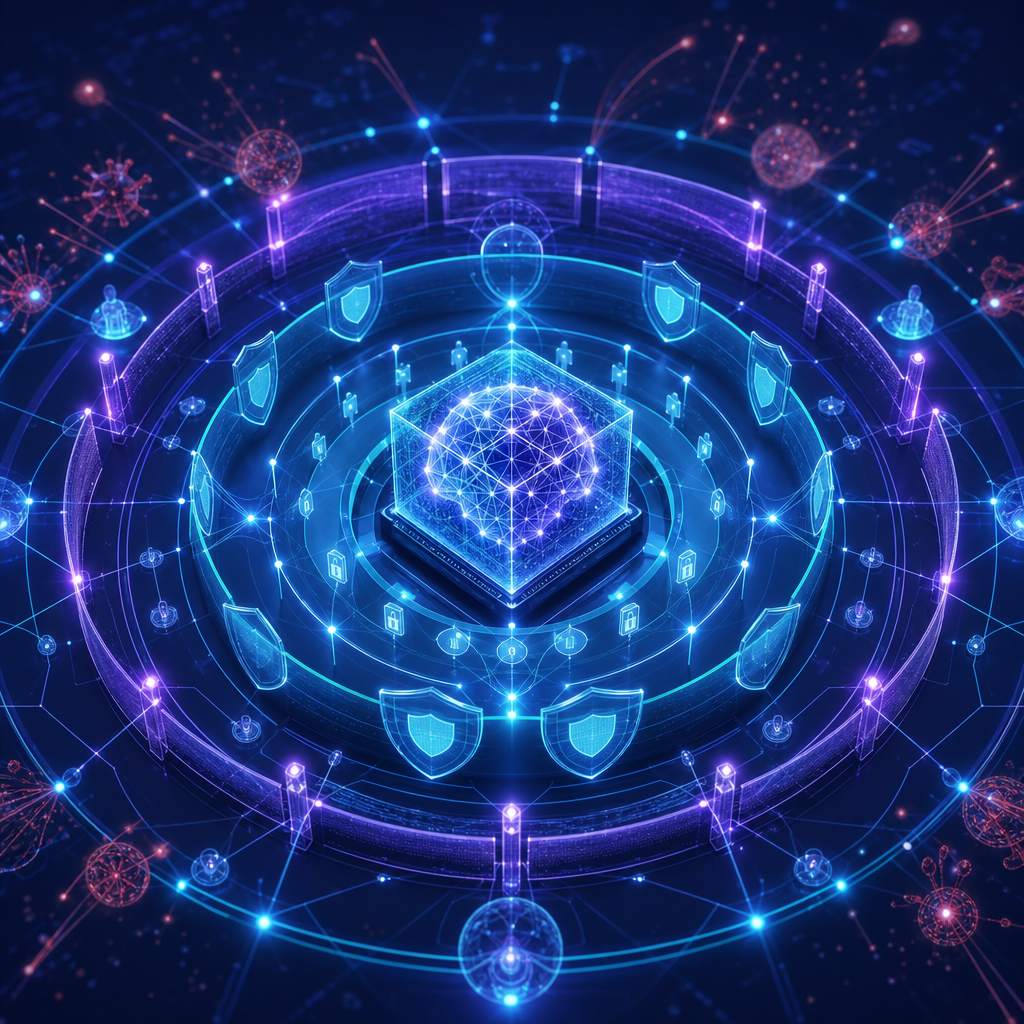
Protected enterprise AI model surrounded by security, privacy, audit, and governance controls
Trustworthy AI by design

The work

Engineering that holds up beyond the demo.

We help large enterprises and AI-enabled product companies identify, test, govern, and reduce the risks introduced by models, data, agents, and AI-enabled workflows. The work connects threat modeling, red teaming, privacy, safety evaluation, regulatory readiness, secure architecture, and operational response into evidence that engineering and executive teams can act on.

What we help you achieve

  • A clear inventory of AI systems, data flows, owners, dependencies, and risk exposure
  • Earlier detection of prompt injection, data leakage, unsafe behavior, misuse, and model failure modes
  • Controls mapped to business risk, regulatory obligations, product context, and deployment reality
  • Evidence-based release decisions with accountable owners, residual risk, and remediation priorities
  • A repeatable AI security and governance operating model rather than a one-time compliance exercise

Detailed capabilities

The work behind a dependable platform.

Explore the engineering areas that take this capability from a first technical decision to a stable, production-ready system.

01

AI Risk & Threat Architecture

Make the AI attack surface visible before controls are designed or systems are scaled.

  • Inventory models, prompts, agents, tools, data sources, vendors, applications, users, and deployment environments
  • Map trust boundaries, identity, data movement, model dependencies, tool permissions, and high-impact decisions
  • Classify risks across confidentiality, integrity, availability, safety, fairness, privacy, misuse, and regulatory impact
  • Define abuse cases, threat scenarios, control owners, risk acceptance, and escalation paths
02

Adversarial Testing & Red Teaming

Test the system as it will actually be attacked, misused, misunderstood, and pushed beyond its intended boundary.

  • Probe prompt injection, jailbreaks, indirect instructions, tool abuse, data exfiltration, and privilege escalation
  • Test retrieval poisoning, malicious documents, unsafe outputs, model extraction, supply-chain exposure, and tenant crossover
  • Build repeatable attack suites with severity, reproducibility, evidence, remediation guidance, and regression tracking
  • Exercise human escalation, fallback, containment, rollback, and incident response procedures
03

Privacy, Safety & Responsible AI Controls

Turn responsible-AI principles into technical controls that can be tested and operated.

  • Apply PII detection, minimization, masking, retention, consent, residency, encryption, and access policies
  • Evaluate harmful content, bias, toxicity, hallucination, copyright, vulnerability, and domain-specific safety risks
  • Define human review, refusal, abstention, explainability, appeal, monitoring, and override patterns
  • Create model cards, data lineage, limitations, usage boundaries, user notices, and audit evidence
04

Compliance Readiness & Release Governance

Build a practical bridge from regulatory requirements to engineering backlogs and release decisions.

  • Map controls and evidence to NIST AI RMF, ISO 42001, EU AI Act obligations, internal policies, and customer commitments
  • Define risk tiers, technical documentation, quality thresholds, approval roles, and change-impact review
  • Gate model, prompt, dataset, retrieval, agent, and application releases on security, safety, privacy, and performance evidence
  • Track findings, exceptions, residual risk, remediation status, ownership, and executive reporting
05

AI Security Operations

Keep controls effective after go-live as models, data, attackers, users, and product behavior change.

  • Monitor model behavior, abuse signals, sensitive-data exposure, policy violations, drift, and anomalous tool use
  • Connect AI telemetry to security operations, incident response, alerting, case management, and audit workflows
  • Establish playbooks for containment, key and access changes, rollback, user communication, and recovery
  • Run recurring control validation, red-team refreshes, tabletop exercises, and governance reviews

Technical scope

Engineering detail from reset to runtime.

The work is designed around observable system behavior: what executes first, how resources are controlled, how failures are recovered, and how the platform proves it is ready.

01

Threat & attack surface

  • Models, prompts, agents, tools, retrieval, data sources, vendors, applications, identities, trust boundaries, and high-impact decisions
  • Prompt injection, jailbreaks, tool abuse, data exfiltration, model extraction, retrieval poisoning, supply-chain, and tenant-isolation risks
02

Privacy & safety controls

  • PII detection, masking, minimization, consent, residency, retention, encryption, access policy, human review, refusal, abstention, and override
  • Harmful content, bias, toxicity, hallucination, copyright, robustness, misuse, domain safety, and user-notice evaluation
03

Governance & compliance

  • NIST AI RMF, ISO 42001, EU AI Act readiness, risk tiers, technical documentation, model cards, lineage, limitations, and approvals
  • Release gates, exceptions, residual risk, control ownership, audit evidence, change-impact review, and executive reporting
04

Security operations

  • Behavior, abuse, sensitive-data, policy, drift, anomalous-tool-use, and runtime telemetry connected to security operations
  • Containment, rollback, incident response, tabletop exercises, recurring red teams, control validation, and recovery playbooks

Services and customer value

Technical work with a business reason.

Every engineering activity is tied to a decision your team needs to make: bring up faster, reduce risk, improve determinism, or prove production readiness.

01

AI risk and threat assessment

Technical work

Inventory AI systems, data flows, dependencies, trust boundaries, threat scenarios, business impact, control gaps, owners, and remediation priorities.

Customer benefit

Leaders get a defensible view of where AI creates material exposure and what to fix before scaling usage.

02

AI red teaming and adversarial testing

Technical work

Exercise prompt injection, jailbreak, tool abuse, data exfiltration, poisoning, tenant crossover, unsafe output, and product-specific attack paths.

Customer benefit

Teams find exploitable behavior with reproducible evidence instead of discovering it through customers or incidents.

03

Responsible AI and privacy controls

Technical work

Implement PII, consent, residency, retention, safety, human oversight, refusal, explainability, data lineage, and usage-boundary controls.

Customer benefit

AI can scale with clear safeguards for sensitive data, vulnerable users, regulated decisions, and customer trust.

04

Compliance readiness and release governance

Technical work

Map NIST AI RMF, ISO 42001, EU AI Act, and internal policy requirements to evidence, risk tiers, approval flows, release gates, and audit trails.

Customer benefit

Compliance becomes an engineering operating model with visible ownership and measurable readiness.

05

AI security operations

Technical work

Connect AI telemetry, abuse monitoring, incident playbooks, containment, rollback, recurring testing, tabletop exercises, and control validation.

Customer benefit

The organization can respond to changing threats and model behavior without treating every event as an improvised crisis.

Fixed-bid project options

Defined scope. Measurable outcomes.

Start with a clearly bounded enterprise engineering program. Each package defines the work, outputs, assumptions, and acceptance criteria before implementation begins.

01Assessment

Enterprise AI Risk & Readiness Assessment

Assess a defined AI portfolio or product surface, its data flows, trust boundaries, threat scenarios, governance posture, and regulatory exposure.

Deliverables

  • AI system inventory and risk classification
  • Threat model and prioritized control-gap register
  • NIST AI RMF, ISO 42001, and EU AI Act readiness map
  • Executive remediation roadmap with owners and sequencing

Acceptance criteria

All in-scope systems have documented owners, risks, controls, evidence gaps, priorities, and an agreed remediation backlog.

02Validation sprint

AI Red-Team & Safety Validation Sprint

Test one defined model, agent, RAG workflow, or AI-enabled product against agreed adversarial, safety, privacy, and misuse scenarios.

Deliverables

  • Reproducible adversarial test suite and severity model
  • Attack evidence, reproduction steps, and remediation guidance
  • Safety, privacy, and misuse evaluation report
  • Regression cases and release-gate recommendations

Acceptance criteria

The agreed scenarios are executed, findings are reproducible, severity is assigned, and every critical finding has a disposition.

03Architecture program

AI Governance & Release Control Blueprint

Design the operating model for risk review, evidence, approvals, monitoring, incident response, and controlled AI releases.

Deliverables

  • Governance roles, decision rights, and risk-tier model
  • Control catalogue and evidence requirements
  • Release-gate, exception, and audit workflow
  • Runtime monitoring and incident-response blueprint

Acceptance criteria

Stakeholders approve the operating model, control ownership, release workflow, evidence checklist, and implementation sequence.

Why this matters for AI

Intelligence needs a dependable execution layer.

AI risk is not solved by a policy document or a one-time penetration test. We connect security architecture, model behavior, data governance, human oversight, compliance evidence, and runtime operations so enterprises can scale AI with accountable controls and product companies can ship AI features without turning trust into a future liability.

What you take forward

Clear outputs your team can build on.

  • AI inventory, risk taxonomy, threat model, abuse cases, data-flow map, control-gap register, owners, and remediation roadmap
  • Adversarial testing suite with prompt injection, jailbreak, tool abuse, exfiltration, poisoning, misuse, privacy, and safety scenarios
  • Privacy, safety, and responsible-AI control package with lineage, PII handling, human oversight, refusal, limitations, and model cards
  • Compliance readiness pack mapped to NIST AI RMF, ISO 42001, EU AI Act, internal policies, approvals, and audit evidence
  • AI security operations handoff with monitoring, containment, rollback, incident, tabletop, recurring testing, and recovery runbooks

Capability map

Built across the layers.

The right answer is usually a connected system of decisions, not a single isolated skill.

01

AI system inventory, threat modeling, attack-surface analysis, and risk classification

02

Prompt injection, jailbreak, data-exfiltration, supply-chain, and agent tool-use testing

03

Privacy, PII, data residency, retention, consent, and access-control engineering

04

Safety, robustness, bias, misuse, toxicity, copyright, and human-oversight evaluation

05

NIST AI RMF, ISO 42001, EU AI Act, secure SDLC, audit, and policy readiness

06

Security telemetry, incident response, monitoring, release gates, and rollback controls

Keep exploring

See how the pieces connect.